Securing sensitive data with granular user roles
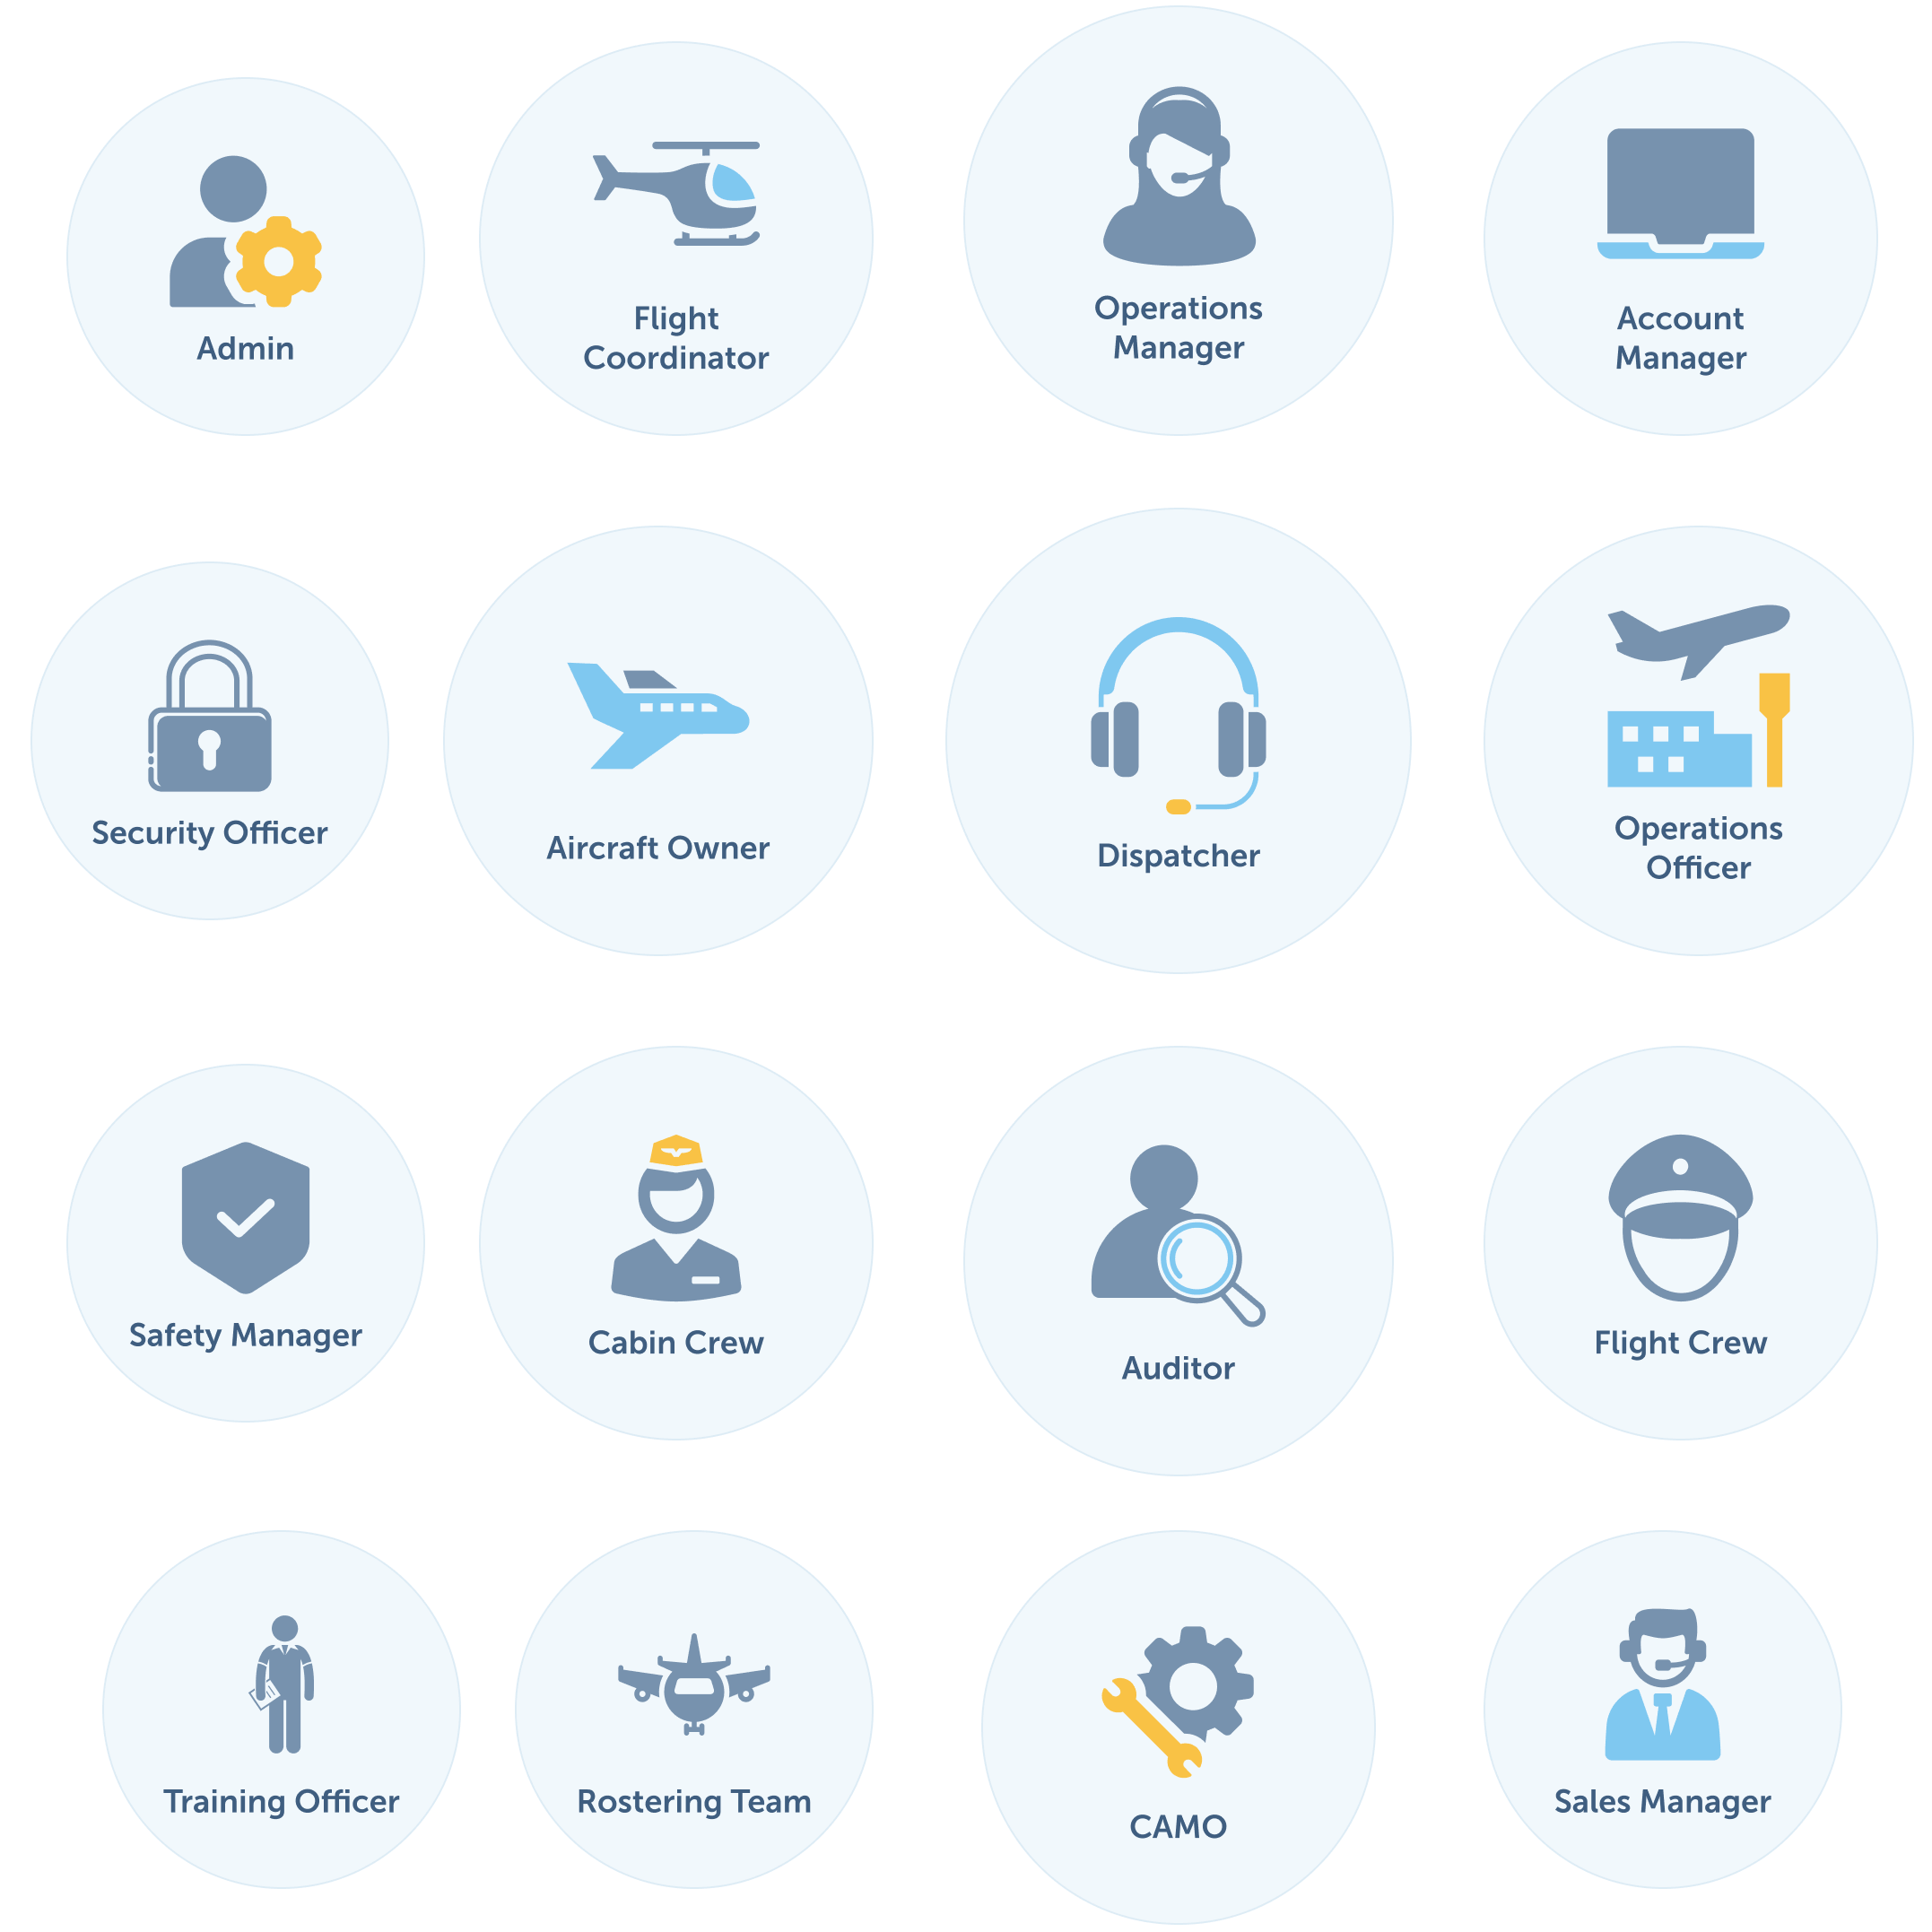
Forcing users into rigid software roles creates an immediate control issue. Standardising permissions into broad categories like “pilot” or “admin” can result in staff having access to more information than they need. This exposes sensitive commercial data and compromises accountability across departments. To maintain strict control, system access must map exactly to the real-world organisational structure, ensuring users interact only with the specific information required to execute their duties safely.
The consequence of predefined permissions
Software relying on predefined user buckets introduces vulnerabilities. For example, if an operations manager needs to update flight checklists, systems frequently require granting them full administrator keys. This inadvertently provides the power to alter company-wide settings, change billing details, or delete users.
Giving staff broad access complicates audit trails and compromises data integrity, while heavily restricting access creates bottlenecks that force employees into workarounds. True control is possible by tailoring permissions precisely to individual duties.
Creating exact boundaries with custom roles
The administration module in Skylegs addresses this by removing predefined limits, allowing administrators to create unlimited custom user roles. For every module and subsection, administrators assign distinct viewing and editing rights.
For instance, an aircraft operator can build a role granting full editing capabilities within the operations module while restricting access to finance modules entirely. Admins track user activity to see exactly who made changes. This exact mapping protects sensitive information and ensures accountability during audits.
Exposing team members to irrelevant data also increases cognitive load and invites human error. For example, generic pilot roles often mean crew members gain access to the entire company document library. A pilot flying a King Air ends up scrolling past manuals meant for a Citation. Through Skylegs’ document control features, access to specific manuals is mapped to the exact aircraft variant a user is qualified to fly. The pilot’s Electronic Flight Bag app syncs only relevant documents, tracking downloads to ensure compliance without cluttering the device.
Conclusion
System security and operational clarity depend on exact permission management. By configuring granular user roles, operators eliminate the hazards associated with broad access and ensure every action within the system is intentional and traceable. This approach protects commercial data, simplifies compliance tracking, and provides team members with a focused, relevant interface to perform their duties safely.
